
IP fraud scores can help explain why a particular connection is subject to extra scrutiny, but the score alone rarely tells the whole story. This guide explains the factors that affect an IP fraud score, how to interpret it, who should review it, which detection tools to use, and how to respond when an IP is flagged.
What is an IP fraud score?
An IP fraud score is a numerical estimate of the risk of fraudulent activity associated with an IP address. When you check an IP with a fraud-detection service, a higher score generally indicates higher perceived risk. Sites that use IP risk scoring may require additional verification, restrict access, or block registrations and payment attempts based on the score combined with other security signals.
However, a high score by itself does not prove the current user committed fraud. IP fraud scores reflect a range of risk signals. Understanding those signals helps explain why an IP address received a high score and what aspects may merit deeper investigation.
What factors influence an IP fraud score?
An IP fraud score can be affected by the IP’s abuse history, the type of network, and observed activity patterns. Some scoring systems also incorporate contextual information from the visitor or transaction to enrich the assessment.
Abuse history and IP reputation
Past associations with spam, account takeover attempts, or fraudulent transactions can raise an IP’s risk rating. Recent incidents and repeated abuse are particularly influential. Keep in mind that an IP’s history reflects prior users or others on the same network, not necessarily the current connection.
Use of proxies, VPNs, and Tor
Proxies, VPNs, and Tor hide a user’s originating IP and can affect fraud scores because they obscure identity and location. These connections often receive heightened scrutiny even though they also serve legitimate privacy and business needs. The presence of an anonymizing service alone does not constitute proof of fraud.
Network type and shared usage
Knowing whether an IP belongs to a residential ISP, mobile carrier, business network, or data center adds useful context. For example, many users may legitimately share a company’s public IP. Network type and shared usage explain traffic patterns but do not make a connection inherently safe or suspicious on their own.
Unusual activity patterns
Large volumes of transactions from a single IP that reference many different email addresses, billing addresses, or payment cards can raise alerts. Anti-fraud systems use frequency checks to evaluate transaction volume over a period. The combination of volume, timing, and shifting details often reveals patterns worth investigating.
Associations with high-risk devices or accounts
When an IP is linked to devices, emails, or accounts already associated with suspicious activity, its risk rating may increase. These associations go beyond the IP’s isolated history and help identify related fraud attempts. Such links are based on observed behavior rather than intrinsic IP attributes.
Location and user context
Location mismatches between the estimated IP location and information provided in a transaction can prompt further checks. For example, if the connection source is far from the stated billing address, that discrepancy may trigger verification. This comparison requires additional user or transaction data and is part of broader fraud assessment rather than a simple IP lookup.
How to interpret an IP fraud score
An IP fraud score consolidates multiple risk signals into a single value. When reviewing results, confirm how the scoring tool defines its scale. Many tools use a scale roughly between 0 and 100, where higher values indicate greater risk; however, thresholds for low, medium, and high risk vary between providers. An 80 does not necessarily mean an 80% probability of fraud.
Risk levels reported by IP fraud tools can guide whether a connection requires further attention:
| Risk level | Typical meaning | Suggested response |
| Low | Few or weak risk signals detected. | Proceed with standard checks; low score is not a guarantee of safety. |
| Medium | Some indicators suggest the connection warrants further review. | Examine flagged details and consider additional verification. |
| High | Multiple or stronger risk signals present. | Require further verification or manual review before proceeding. |
| Very high / Critical | The scoring system identifies significant risk. | Consider restricting activity while you investigate the evidence. |
IP fraud scores can change as detection systems receive new signals. Past scores provide helpful context but should not be treated as a permanent label for an IP address.
What to do if your IP fraud score is high
To improve or address an elevated score, start by identifying why the rating rose and investigate the activity behind it. The following checks help you decide whether to continue using the connection:
- Check the same IP with another fraud-scoring tool.Enter the same public IP into different services and compare risk levels and findings. Identical numeric scores can mean different things across providers. If one service reports recent abuse while another shows a low score, investigate the abuse report rather than dismiss it.
- Identify the causes behind the score.Look for indicators such as recent abuse reports, unusual traffic, or proxy/VPN flags. Labels describe how the IP is used, while abuse reports describe actions tied to it. Dates and descriptions help prioritize what to examine.
- Investigate activity on the network.If you manage the network, review security logs and connected devices for unexplained traffic. If the IP belongs to an ISP, proxy, or VPN provider, forward the IP and reports to them for further investigation, since shared IPs can reflect others’ behavior.
- Request corrections for inaccurate reports.Verify whether the reported location, network type, or activity is incorrect and contact the reporting service with the IP address, disputed details, and supporting evidence.
- Re-check results and any access restrictions.After investigating or requesting corrections, run the IP through fraud checks again to see if the rating changed. If a site still blocks you, provide the site with error details and connection information—sites may use additional signals beyond public scoring tools when making decisions.
Who should review IP fraud scores—and why
IP fraud scores are useful at many points in online interactions. Businesses often check IPs for payments, logins, or lead validation. Users who rely on proxy services or who repeatedly encounter verification prompts may also want to inspect their public IP. In each case, the score provides a data point to inform decisions.
E-commerce and payments teams
Online stores can query an IP score when an order looks unusual. If the IP has recent abuse ties, payment teams can weigh that finding against order details and customer history to decide before approving a transaction, reducing fraud while minimizing friction for legitimate customers.
Account security and fraud teams
These teams use IP checks during account creation and login. IPs linked to automated attacks deserve special attention, especially when combined with unfamiliar devices or odd login patterns. Security teams then decide whether to require additional verification to protect accounts.
Marketing and lead-generation teams
IP fraud scores help evaluate leads from marketing and affiliate partners. If a partner suddenly sends a spike of submissions from suspicious IPs, teams can investigate before accepting leads or paying commissions. The score is part of screening; submission patterns and lead details complete the picture.
Proxy and VPN users
For proxy and VPN users, the relevant IP is the public exit IP seen by websites. Checking an IP fraud score lets users determine whether that exit IP is flagged for recent abuse or merely identified as a proxy/VPN. Distinguishing these scenarios helps users decide if the connection is suitable for work, shopping, or account access.
Users encountering unexpected verification or access issues
If you’re repeatedly asked to verify your identity, check your public IP. Fraud reports can reveal risk signals tied to the address, including activity by others on a shared network. While sites decide when to prompt verification, this information can help you troubleshoot the cause.
IP fraud scoring tools: features, pricing, and use cases
For occasional checks, online lookup tools are convenient. For hundreds or thousands of checks, compare API and bulk-query offerings. Below are three representative options and scenarios where each fits well.
Scamalytics
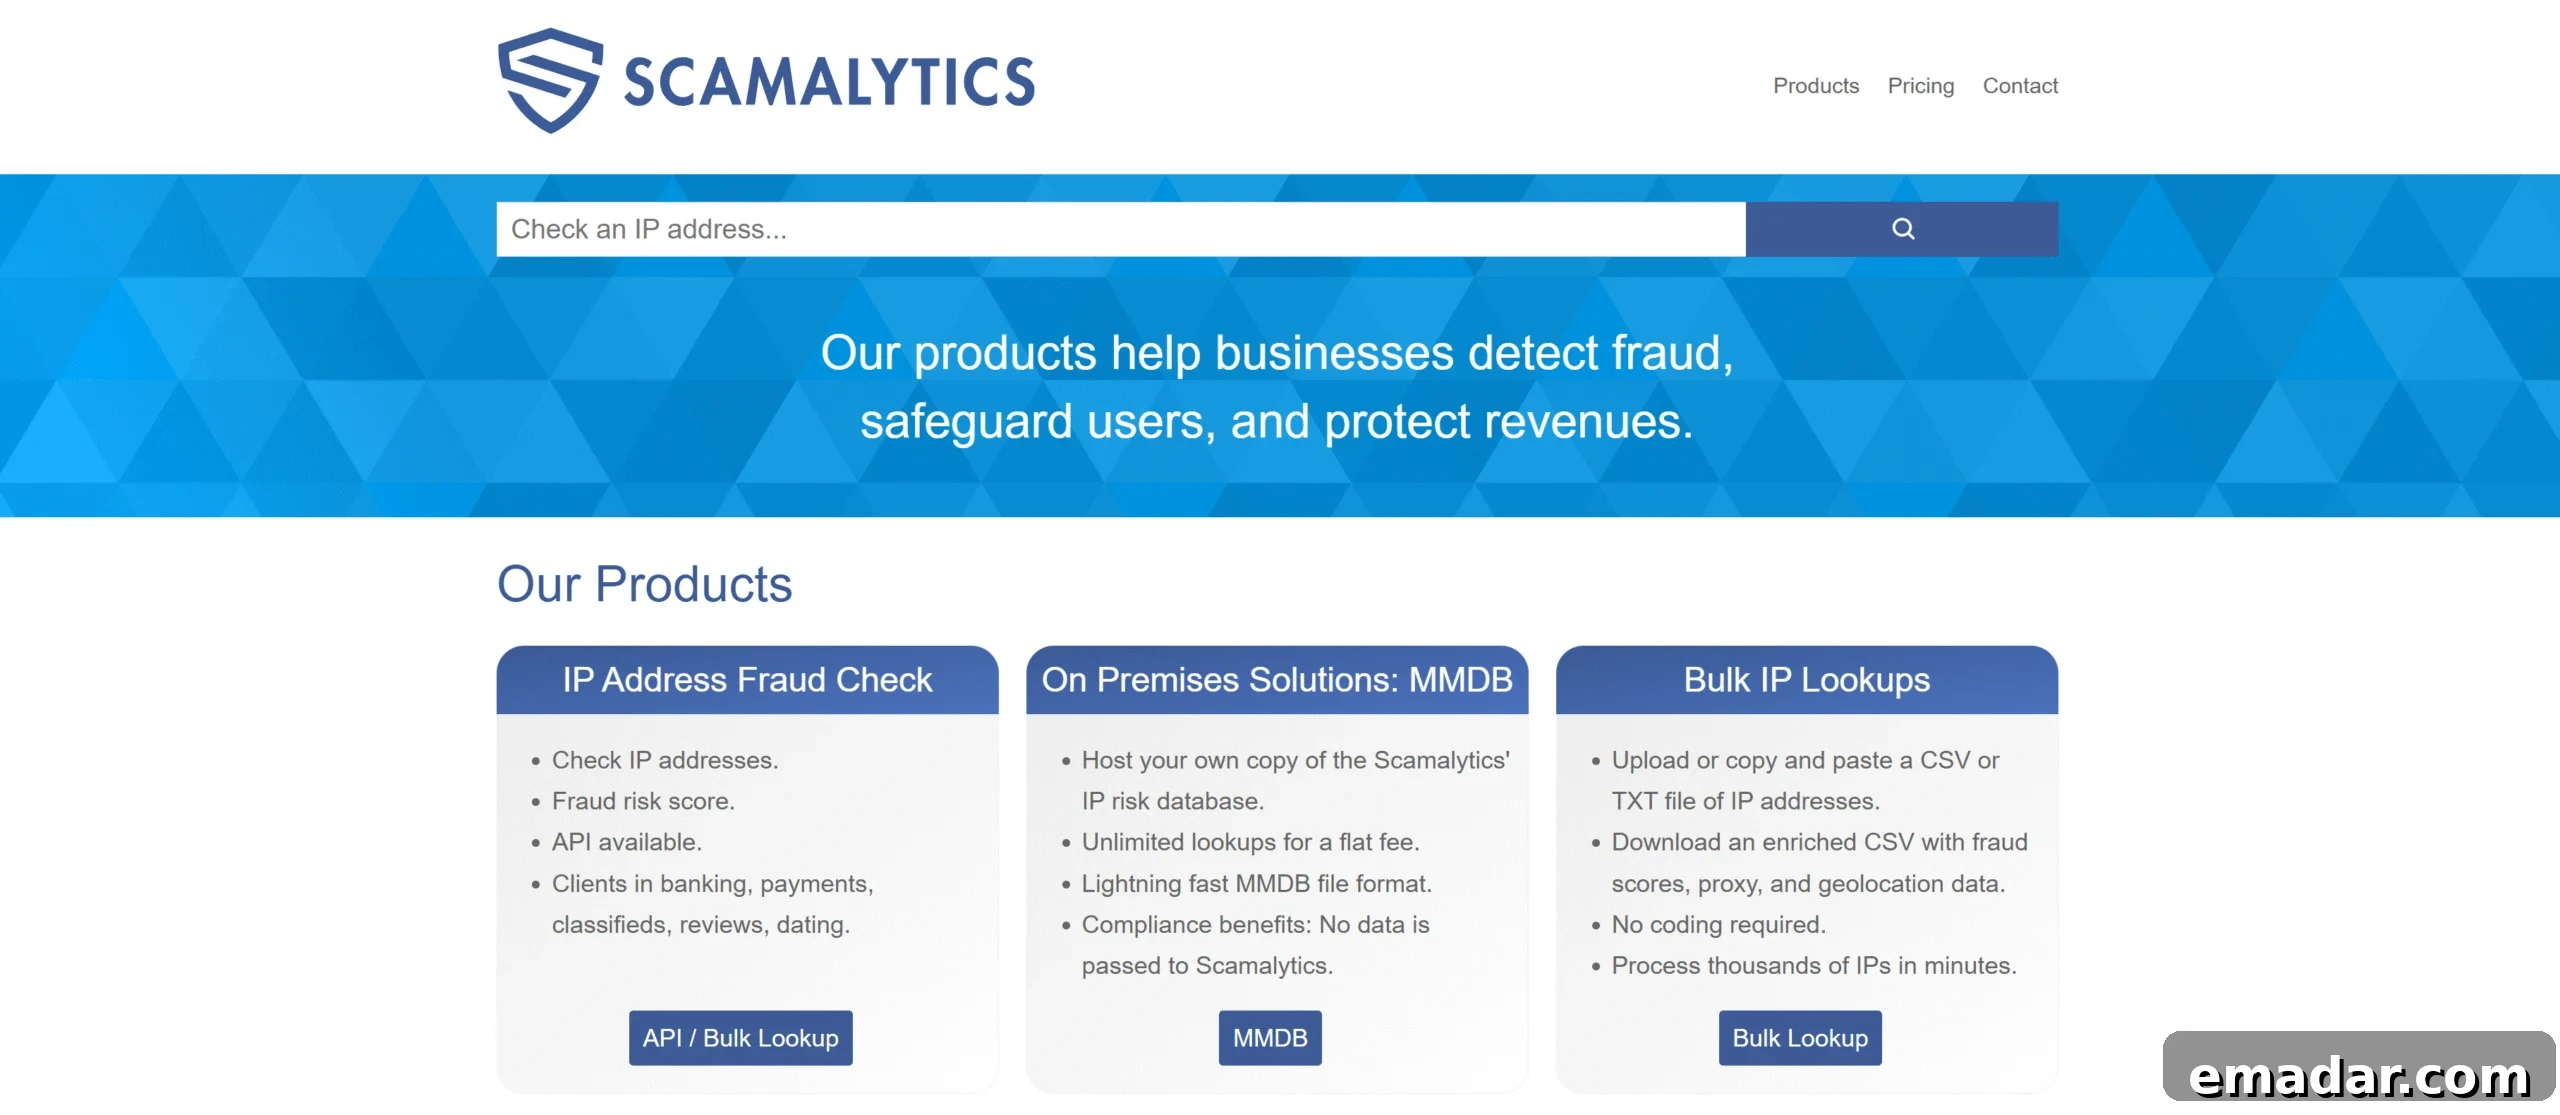
Scamalytics centers its IP service on fraud scores, making it easy to view an address’s risk rating and basic context.
- What it shows: Fraud score, country, network operator, proxy status, and Tor status.
- Pricing: Online lookups are available on the site. The public API offers a free tier with 5,000 monthly requests; a $25/month tier includes 25,000 requests. Some advanced data requires paid add-ons.
- Best for: Individuals checking single IPs and teams seeking an affordable way to check multiple addresses.
IPQualityScore
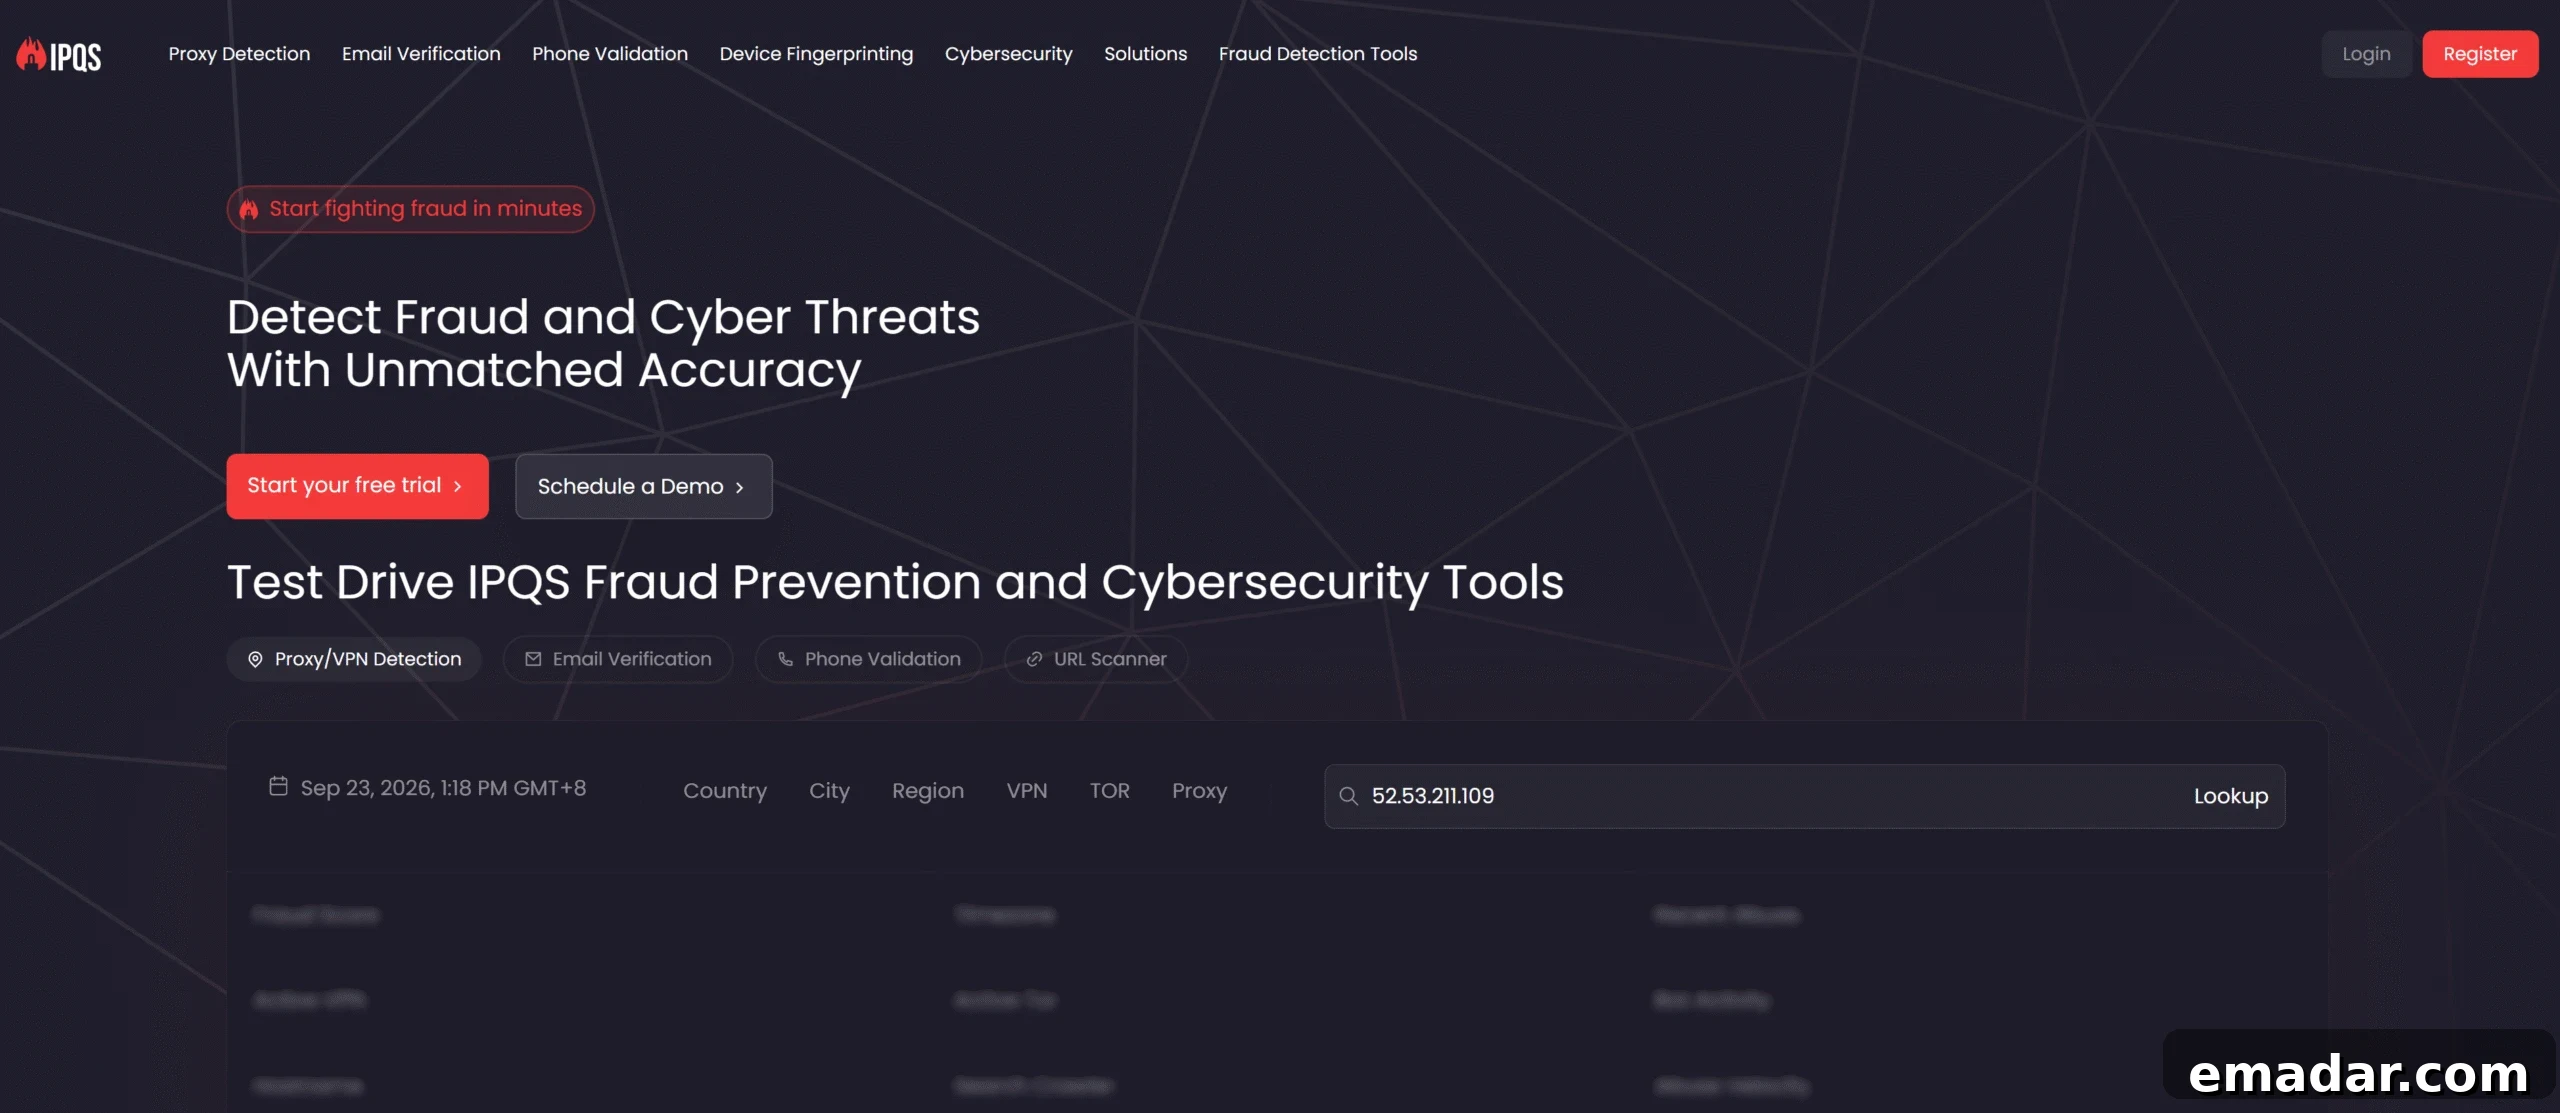
IPQualityScore provides detailed context when a score raises questions, including connection type and abuse indicators.
- What it shows: IP risk details, proxy/VPN detection, connection type, and recent abuse signs.
- Pricing: Free online lookups are available. The free account includes 1,000 monthly queries (daily limit 35). Entry-level plans start at $99/month for 5,000 monthly queries.
- Best for: Security teams reviewing suspicious registrations, logins, or payments when they need more detail than a single score provides.
IP2Location
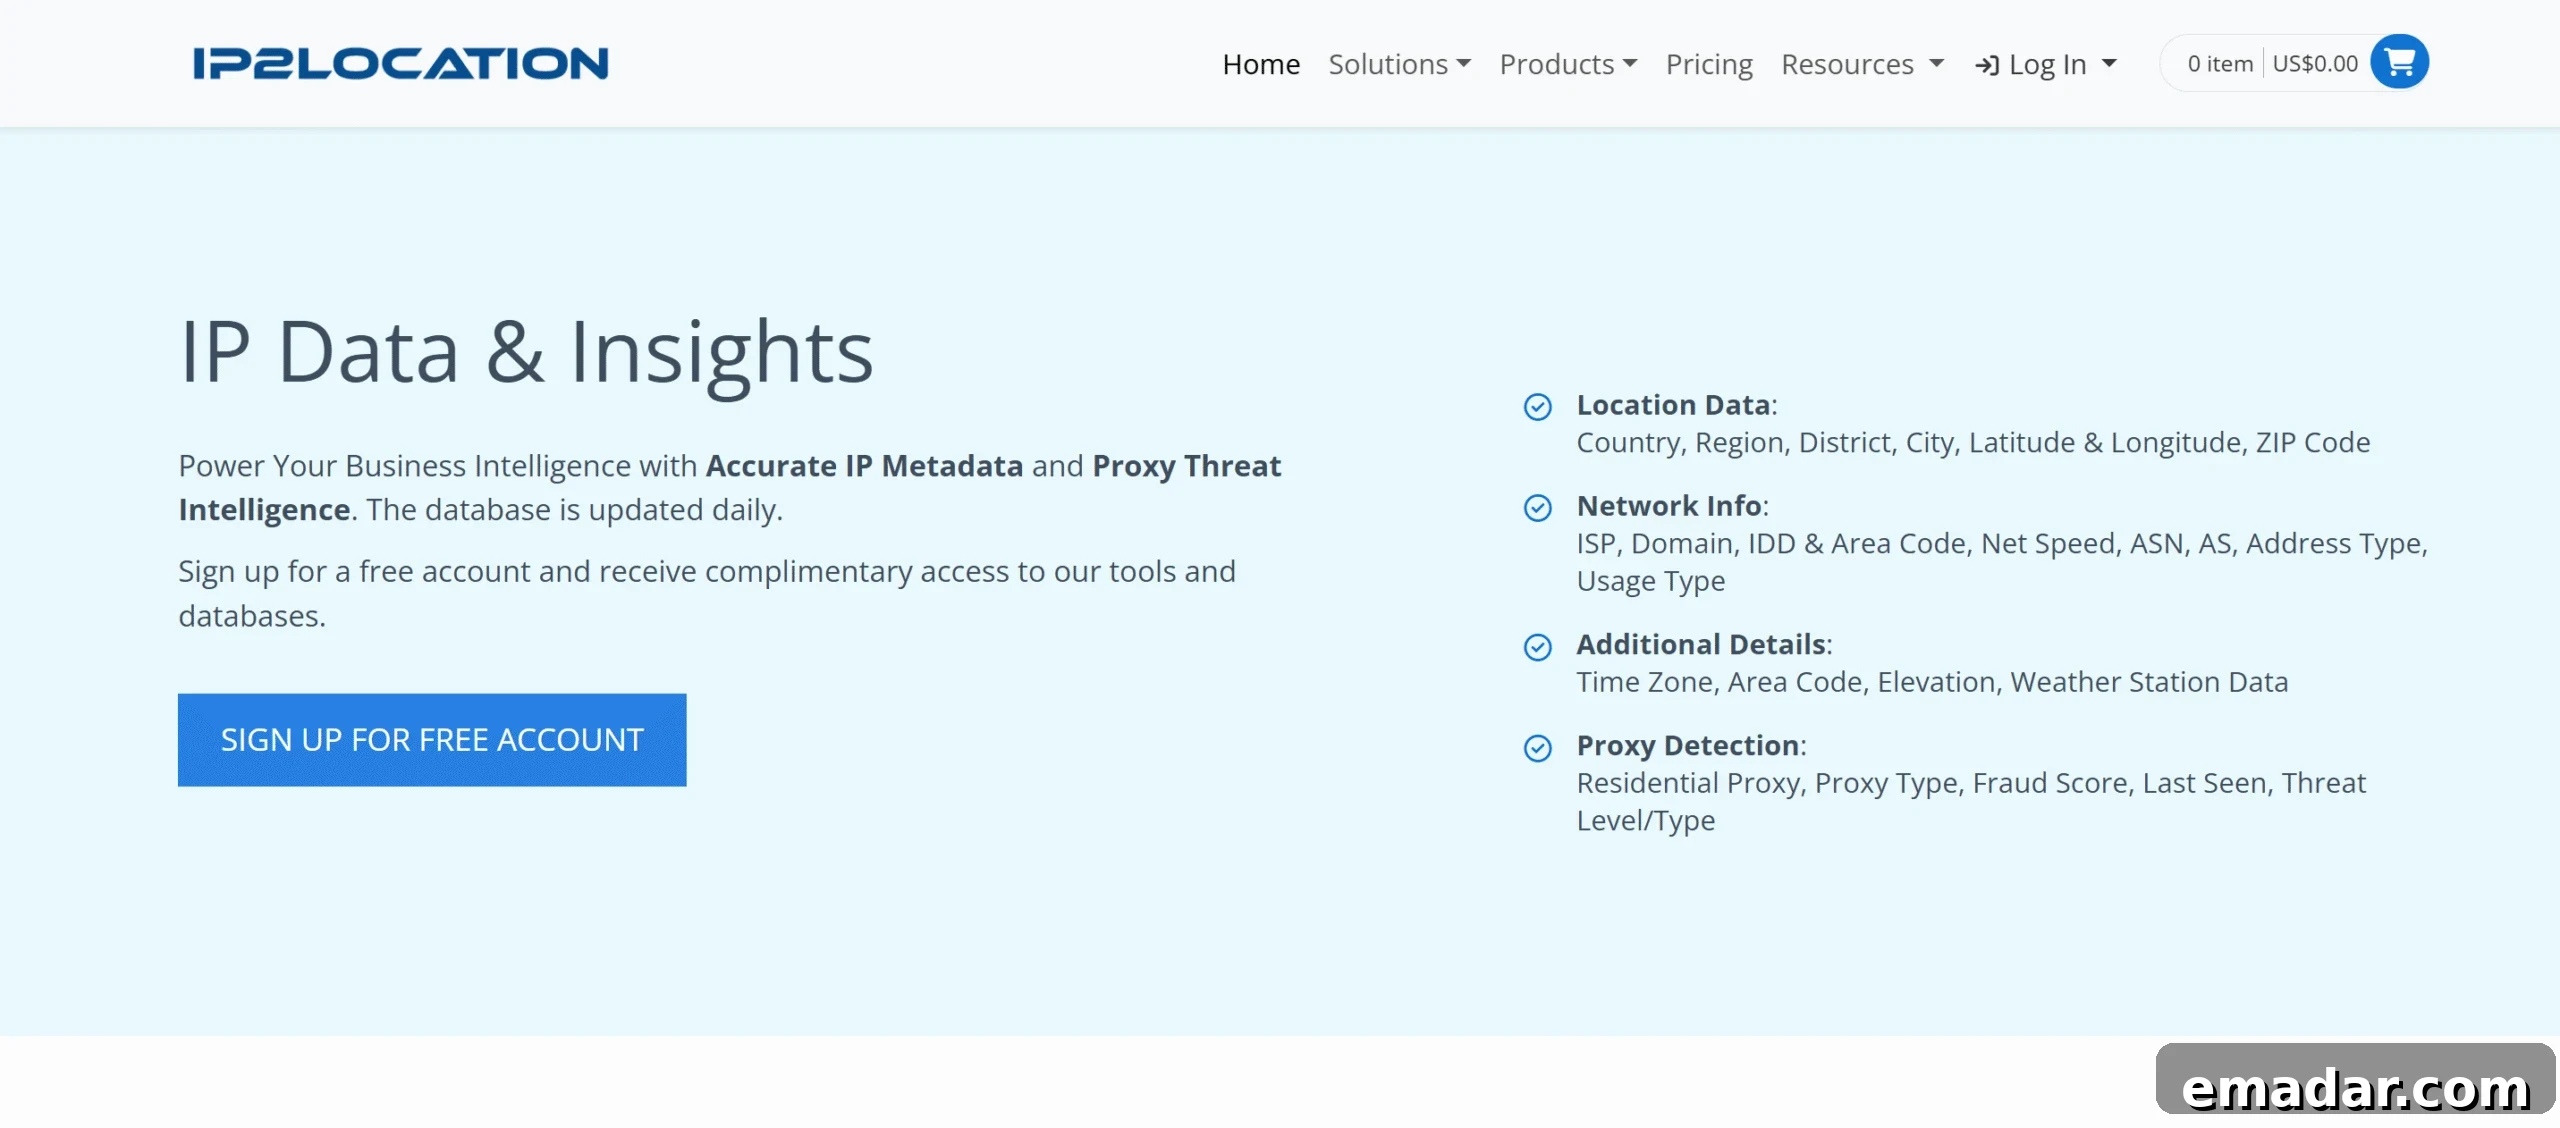
IP2Location is primarily an IP data provider, useful for analyzing network and proxy details associated with an address.
- What it shows: Geolocation, ISP, proxy details, and in some products (like IP2Proxy PX12) a fraud score—don’t confuse the PX12 fraud metric with the standard free lookup fields.
- Pricing: Online lookups are free and PX12 LITE is available. Commercial database pricing varies by product and coverage.
- Best for: Developers and analysts who need IP or proxy data for their systems or who want to combine IP2Location’s data with other services’ fraud scores.
Checking an IP fraud score is straightforward: enter the public IP into a lookup tool and review the results. If you’re using a proxy or VPN, use its exit IP—the address the website actually sees.
Recommendations for maintaining a safer IP environment
Everyday network hygiene can reduce suspicious activity tied to your public IP and make it easier to understand score changes:
- Keep managed devices and networks secure. Update software and investigate unexplained traffic. If a device is compromised, it could send malicious traffic from your public IP; simply changing the IP won’t fix an infected device.
- Use proxies you can manage and audit. If you rely on proxies, check the assigned exit IP and its reported risk before using it for accounts or payments. No provider can guarantee a fixed score in every lookup.
- Record checks when the score matters. Log the IPs you checked, the tools used, results, and dates. If the score changes or a site begins requiring verification, these records provide a starting point for investigation.
Conclusion
An IP fraud score is a starting point for assessing a connection’s risk. Review the reasons behind a score, compare different reports when needed, and investigate unusual activity before deciding how to act. If you use proxies in work contexts, consider the proxy options available and verify the assigned exit IP meets your needs.
Frequently Asked Questions
What does an IP fraud score mean?
An IP fraud score estimates the risk associated with an IP address. A higher score usually means the detection tool found more signals of concern, but it does not prove the current user is committing fraud.
Is IPQualityScore reliable?
Yes. IPQualityScore is an established fraud-detection service with IP fraud scoring capabilities. Its outputs help assess risk, but you should review the detailed report before making decisions.
What is a good IP fraud score?
Lower scores indicate lower risk in general. There’s no universal “ideal” score—check the scoring and risk thresholds used by the specific tool. A low score isn’t a guarantee of safety.
How do I check my IP fraud score?
Find the public IP used for the activity and enter it into an IP fraud lookup tool to view the score and reported signals. If you use a proxy or VPN, check the exit IP—the address seen by websites.
Why do different tools show different results?
Each tool uses its own data sources, scoring methods, and risk thresholds. One tool may include a recent abuse report that another lacks. Compare the underlying findings before deciding whether an IP merits further investigation.